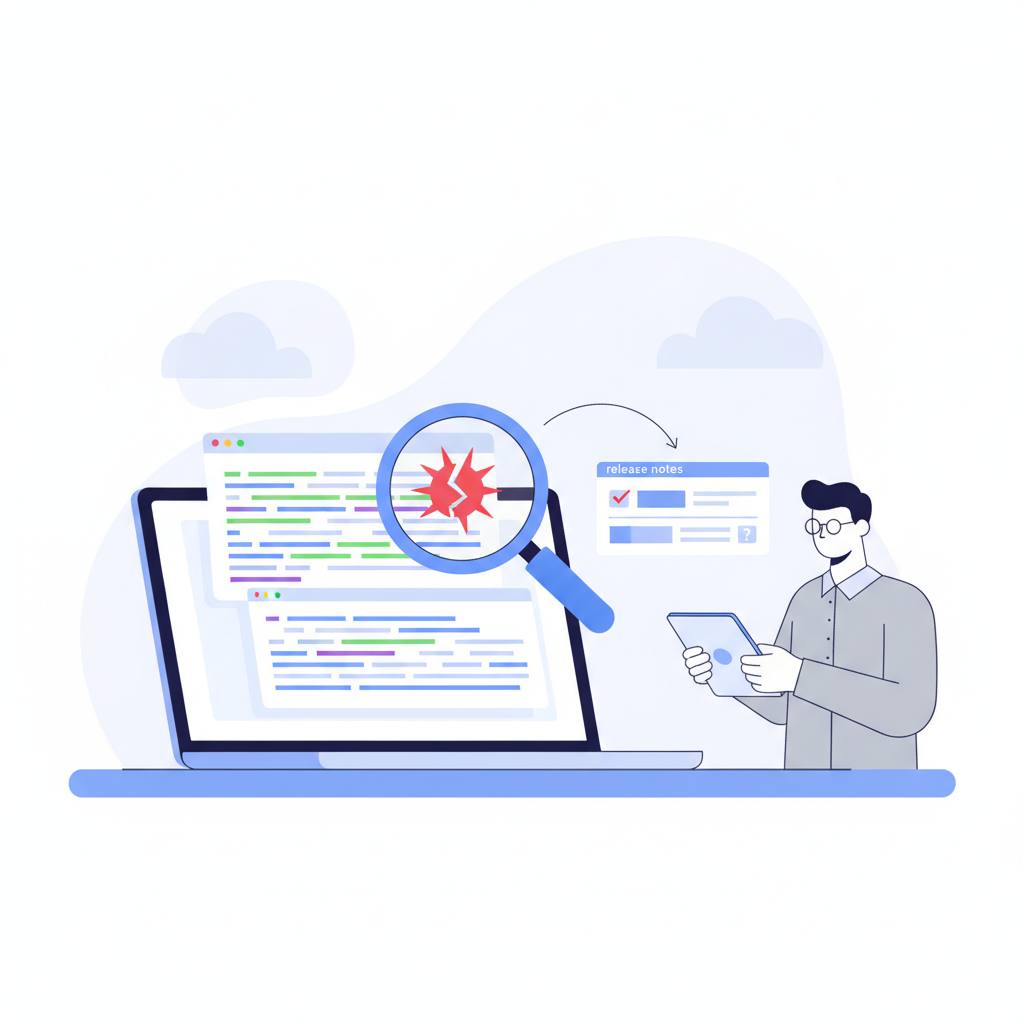
Want to spot software vulnerabilities before they hit the news? Security experts are finding critical flaws by carefully reading release notes, often weeks ahead of official CVE announcements. This proactive approach helps you find potential issues before the crowd.
Hey WondTech readers! Are you tired of chasing software vulnerabilities *after* they hit the news? Here's a pro tip: you can often discover critical flaws weeks before they're announced as official CVEs, simply by reading «release notes» like a security auditor.
What does this mean for you? Well, whether you're a developer, a security enthusiast, or just someone who cares about keeping their software up-to-date, understanding this approach gives you a huge advantage. Instead of just reacting to problems, you can proactively identify potential weaknesses, helping to keep your systems and data much safer.
Traditionally, many vulnerability hunters keep an eye on CVE feeds. That's fine, but here's the kicker: every CVE was preceded by a code commit, a tag, and usually a release note. These notes often appear weeks before the official advisory goes public. Imagine being able to spot a problem before anyone else! That's the core idea. By analyzing these notes with a critical eye, you're not just reacting; you're finding issues before the crowd.
When a software project adds a new authentication mechanism, most people see it as a security hardening step. But a savvy auditor sees it as a «brand-new code path that decides who gets in», often written under schedule pressure and shipped without ever having been attacked. Take, for instance, the 'checkAutoType' function in Java's popular Fastjson library. It was added as a security gate but notoriously became a vulnerability map itself, bypassed over and over for years, with each bypass leading to a new CVE. This illustrates how the defense itself can inadvertently point attackers directly to the target.
So, what signals should you be looking for in release notes?
1. **New Authentication Mechanisms:** As mentioned, scrutinize how strings are compared, look for missing rate limits, and check default-on behaviors. These mechanisms often cover main entry points but might miss newly added internal APIs.
2. **Vague 'Hardening' Language:** When a release mentions general security improvements without much detail, it could be a 'silent fix'. Projects sometimes do this to buy time before a full disclosure. Your move here is to compare code differences between versions to find the specific change and then look for similar code paths that didn't receive the same fix.
3. **Dependency Upgrades (especially Parsers):** A simple one-line mention like «upgrade dependency X» is a red flag, especially if 'X' is a parsing library. This could hide significant changes in how data is processed, potentially introducing new vulnerabilities.
In short, learn to read release notes with a critical, analytical mind. Look for new security features, ambiguously described fixes, and updates to core components. This approach puts you ahead of the curve, making you a discoverer of vulnerabilities, not just a reader of them. Stay safe and smart!
What does this mean for you? Well, whether you're a developer, a security enthusiast, or just someone who cares about keeping their software up-to-date, understanding this approach gives you a huge advantage. Instead of just reacting to problems, you can proactively identify potential weaknesses, helping to keep your systems and data much safer.
Traditionally, many vulnerability hunters keep an eye on CVE feeds. That's fine, but here's the kicker: every CVE was preceded by a code commit, a tag, and usually a release note. These notes often appear weeks before the official advisory goes public. Imagine being able to spot a problem before anyone else! That's the core idea. By analyzing these notes with a critical eye, you're not just reacting; you're finding issues before the crowd.
When a software project adds a new authentication mechanism, most people see it as a security hardening step. But a savvy auditor sees it as a «brand-new code path that decides who gets in», often written under schedule pressure and shipped without ever having been attacked. Take, for instance, the 'checkAutoType' function in Java's popular Fastjson library. It was added as a security gate but notoriously became a vulnerability map itself, bypassed over and over for years, with each bypass leading to a new CVE. This illustrates how the defense itself can inadvertently point attackers directly to the target.
So, what signals should you be looking for in release notes?
1. **New Authentication Mechanisms:** As mentioned, scrutinize how strings are compared, look for missing rate limits, and check default-on behaviors. These mechanisms often cover main entry points but might miss newly added internal APIs.
2. **Vague 'Hardening' Language:** When a release mentions general security improvements without much detail, it could be a 'silent fix'. Projects sometimes do this to buy time before a full disclosure. Your move here is to compare code differences between versions to find the specific change and then look for similar code paths that didn't receive the same fix.
3. **Dependency Upgrades (especially Parsers):** A simple one-line mention like «upgrade dependency X» is a red flag, especially if 'X' is a parsing library. This could hide significant changes in how data is processed, potentially introducing new vulnerabilities.
In short, learn to read release notes with a critical, analytical mind. Look for new security features, ambiguously described fixes, and updates to core components. This approach puts you ahead of the curve, making you a discoverer of vulnerabilities, not just a reader of them. Stay safe and smart!